Adithyan V
Specialized in Vulnerability Assessment, Threat Monitoring, and Web Security Research with a full-lifecycle defensive and offensive security focus.
About
Background & Technical Focus
Key Achievements
Recognitions, disclosures, and milestones
Govt Infrastructure Disclosures
Independently identified and responsibly disclosed security vulnerabilities in Kerala Government web infrastructure through CERT-In, with official Case IDs assigned.
CTF Competition Winners
Secured 1st Prize in a CTF Competition at Red Team Hacker Academy as part of a three-member squad, Team 0day.
Top 4% Global Ranking
Ranked within the Top 4% on TryHackMe, demonstrating practical skills in penetration testing, SOC operations, and defensive security.
Core Strengths
Tactical capabilities and specialized operational focus
Vulnerability Assessment & Pentesting
Identifying, validating, and reporting security vulnerabilities through comprehensive security assessments.
SIEM & Incident Monitoring
Monitoring security events, analyzing threats, and responding to incidents to protect organizational systems.
AI-Assisted Security & Automation
Enhancing security testing through AI agent integration, automated workflows, and advanced offensive security tooling.
Web Application Security
In-depth security analysis and mitigation strategies for modern web application vulnerabilities.
Network Security
Securing networks through traffic analysis, protocol understanding, and identifying network-based threats.
Threat Intelligence
Collecting, analyzing, and interpreting threat data to identify emerging cyber threats and support proactive defense.
Tools & Technologies
Operational technical stack and security platforms
Offensive Security & VAPT
SIEM & Defence
Network Security & Auditing
Threat Intelligence
Malware Analysis
Linux & Infrastructure
Featured Projects
Practical security implementations and simulations
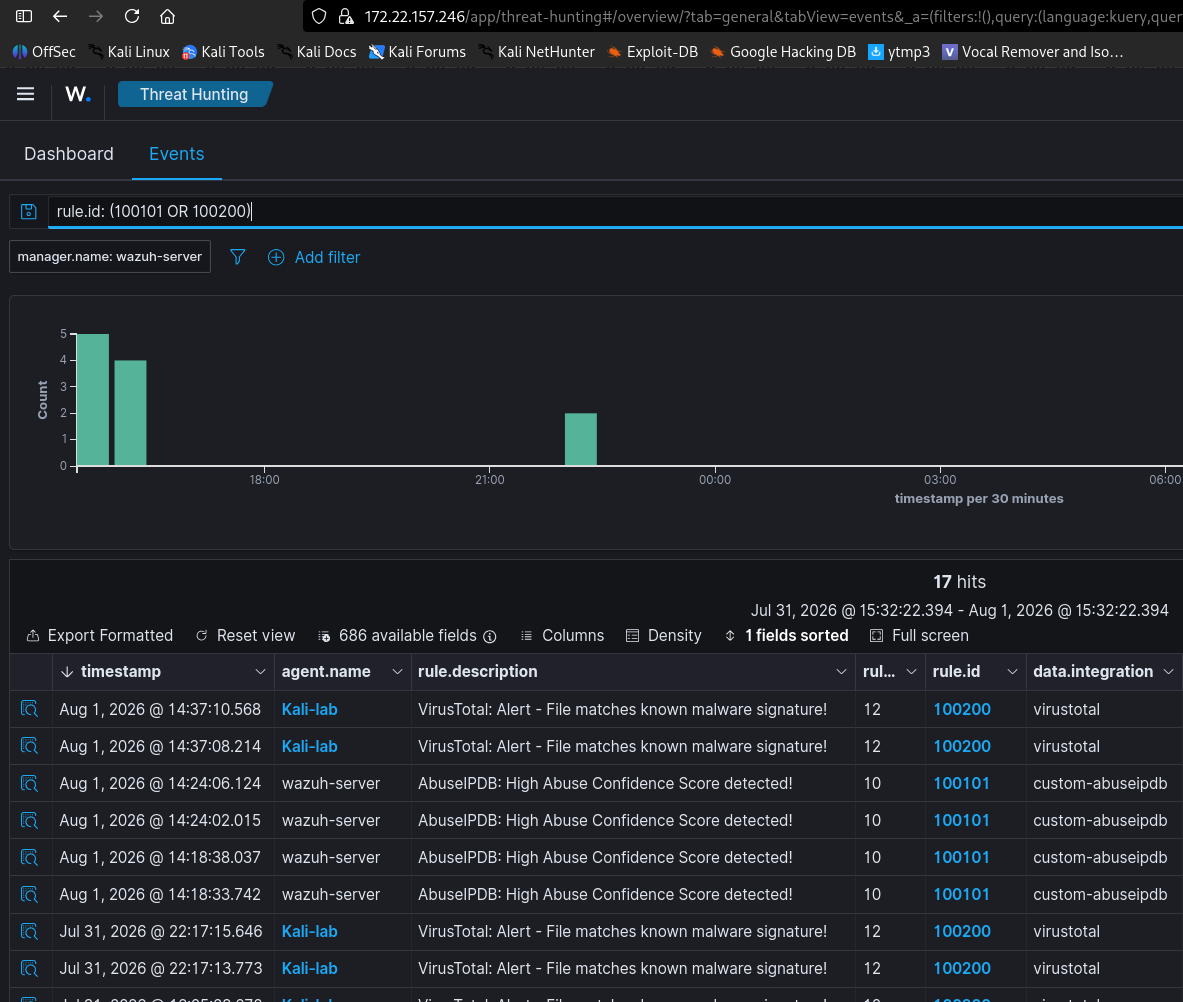
VIPER-SOC
A Wazuh-based automated incident response framework integrating AbuseIPDB & VirusTotal to isolate malicious IPs and remove threats from endpoints in real time.
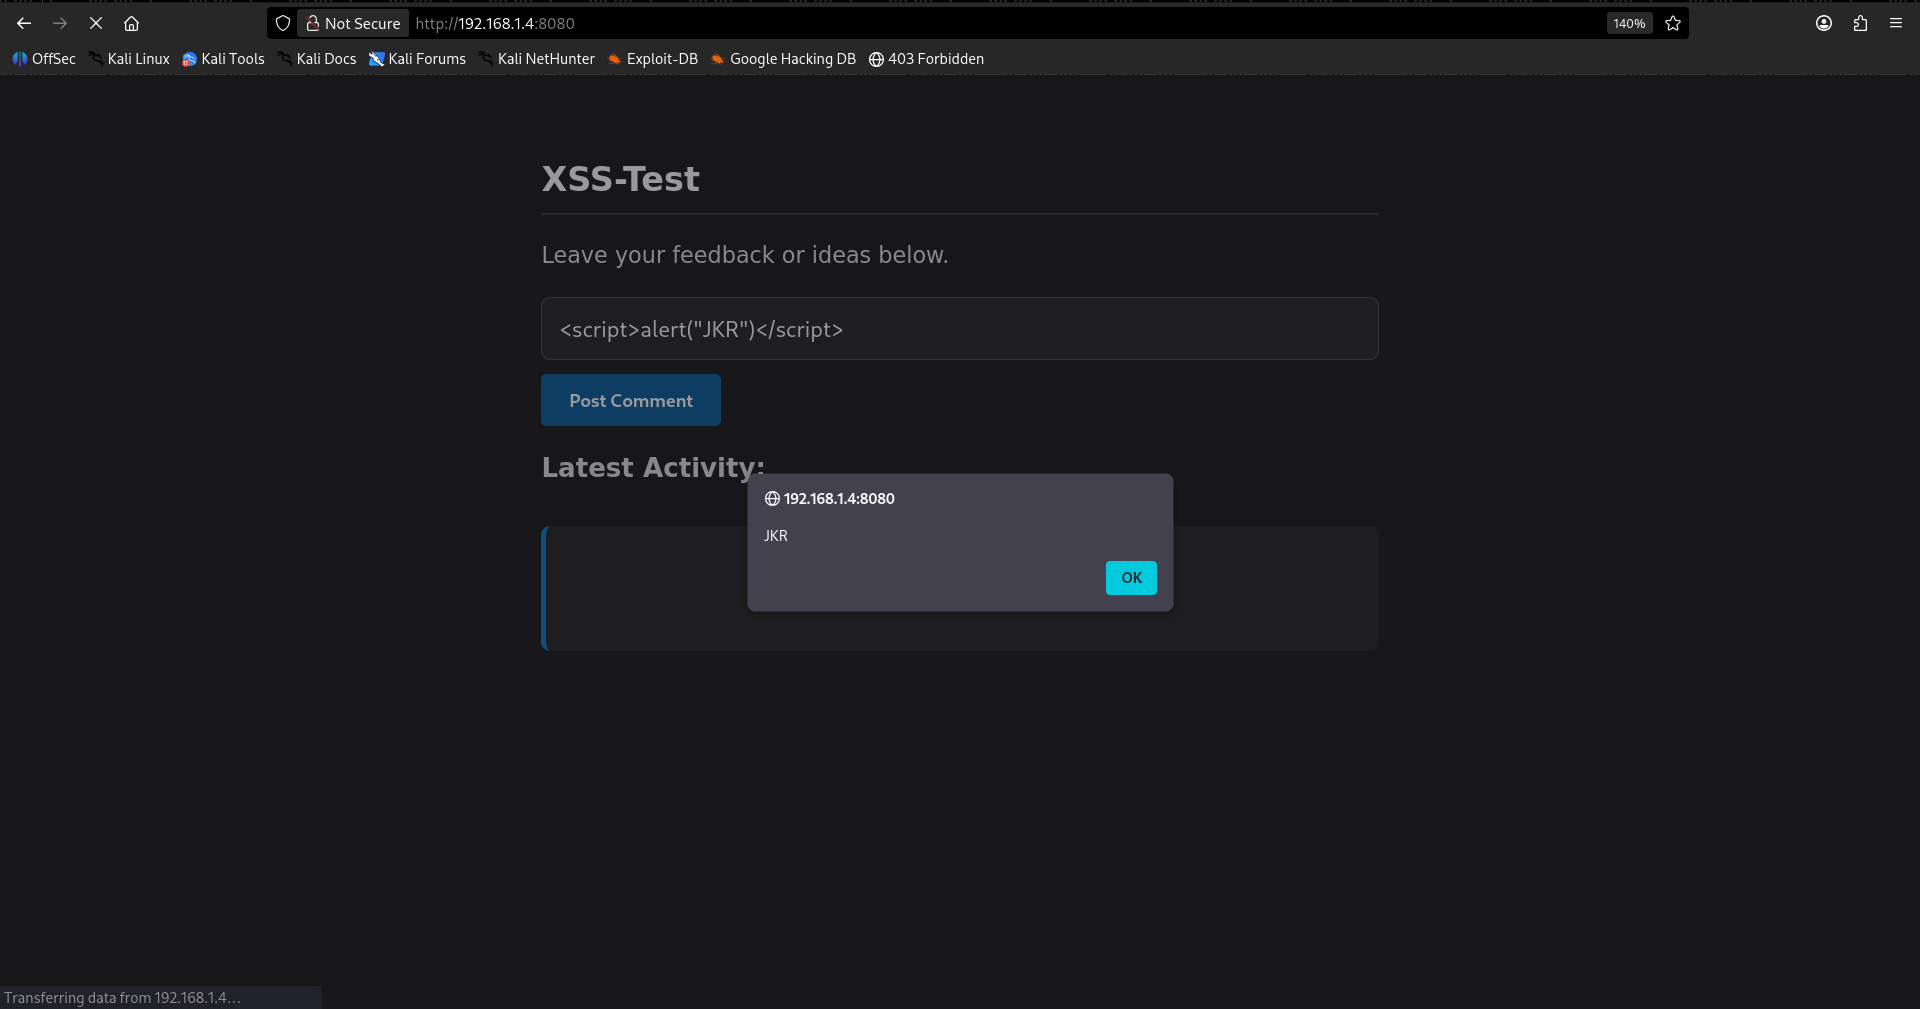
XSS Detection via Snort IDS
Simulated and detected real-time Cross-Site Scripting (XSS) vectors on an intentionally vulnerable Flask web app using Snort 3 custom inspection rules.
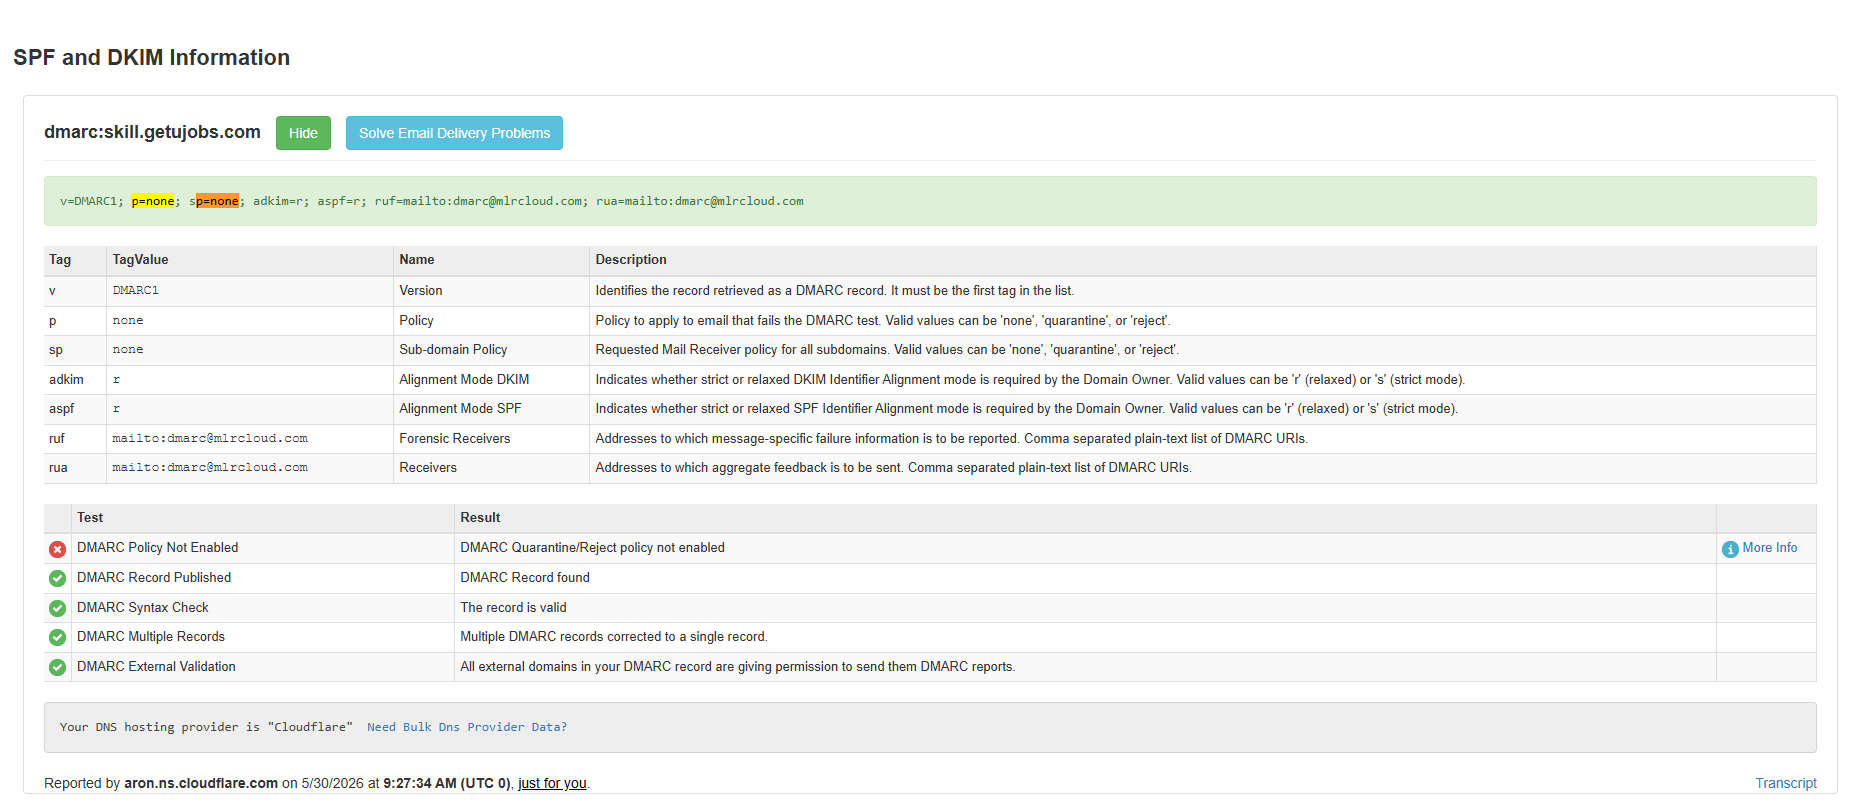
Phishing Threat Detection
Analysis of live email threat vectors, SPF/DKIM header verification via MXToolbox, and threat intelligence mapping to elevate email defense posture.
Education
Continuous path of institutional security foundations and degrees
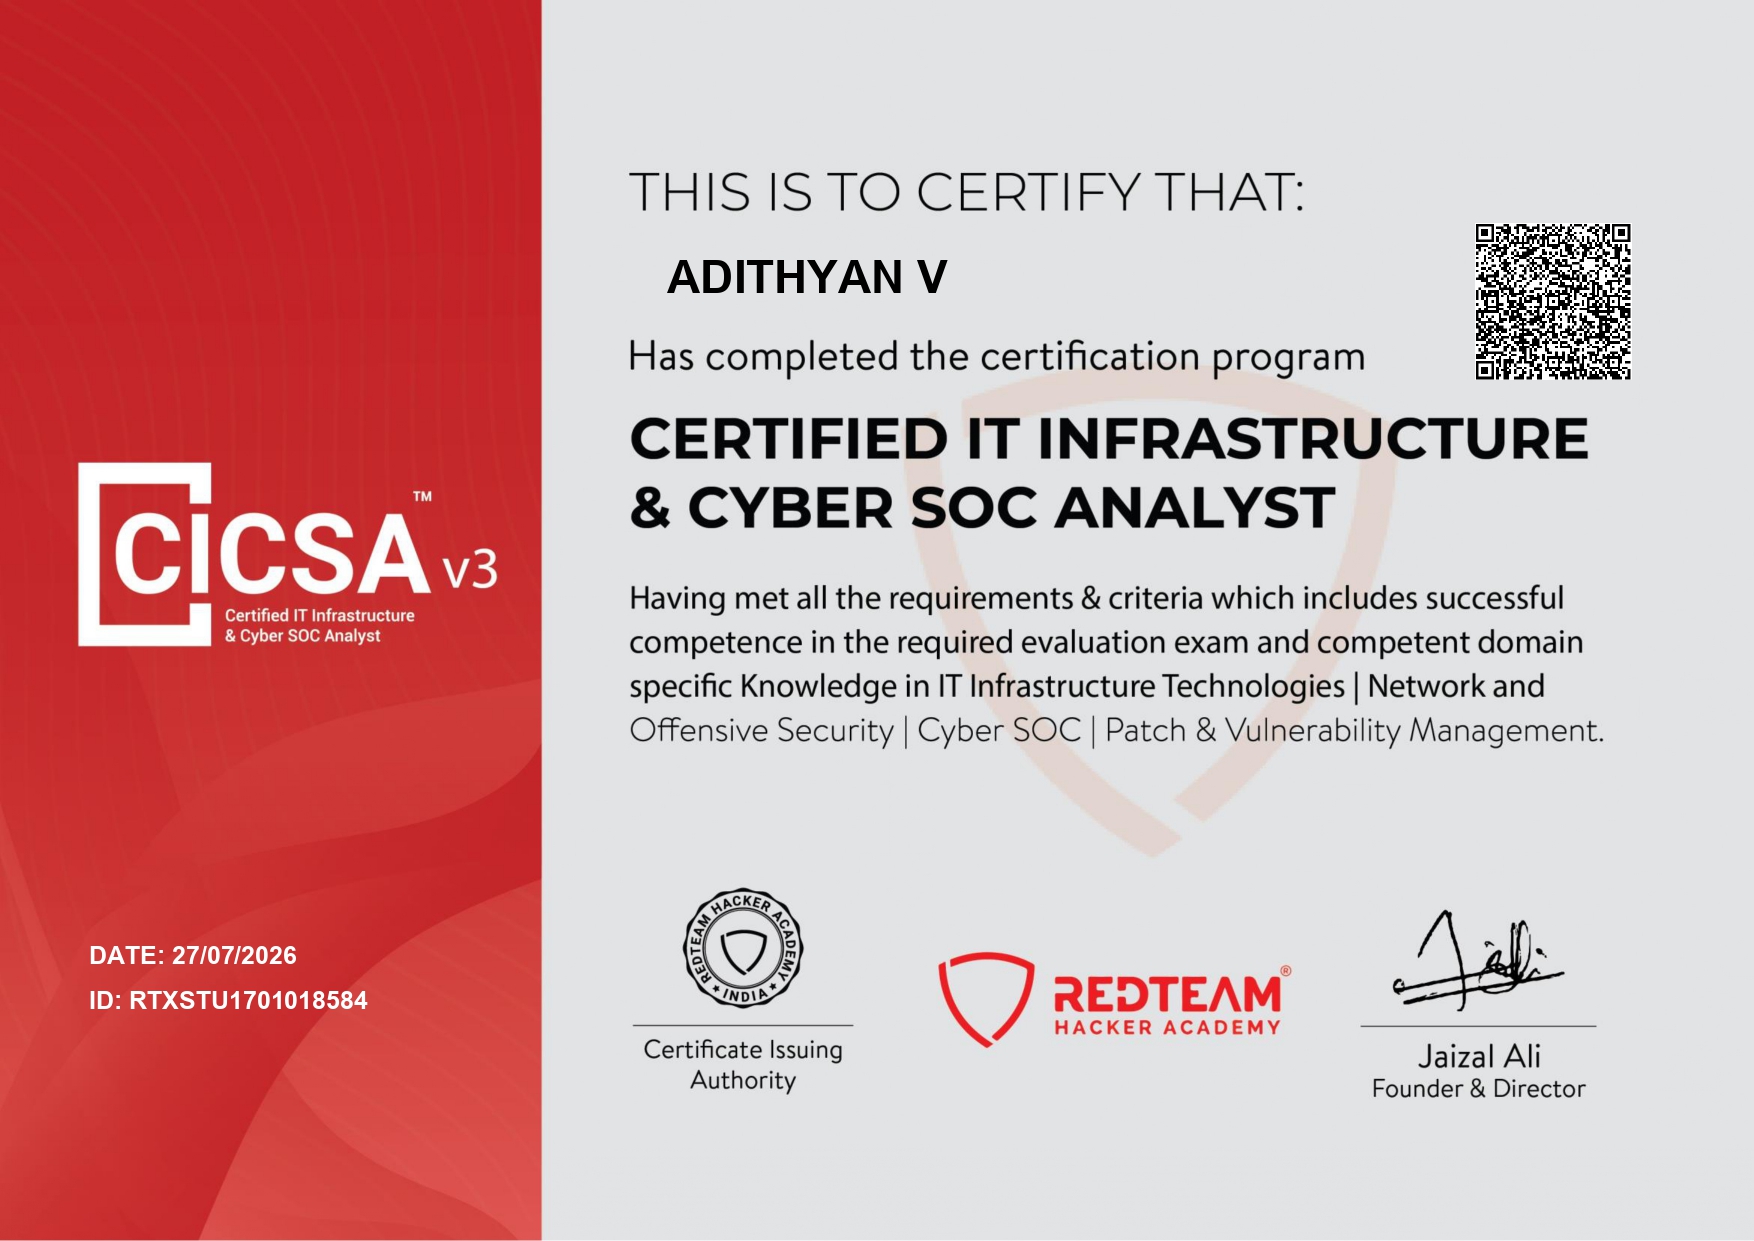
Certified IT Infrastructure & Cyber SOC Analyst
RedTeam Hacker Academy
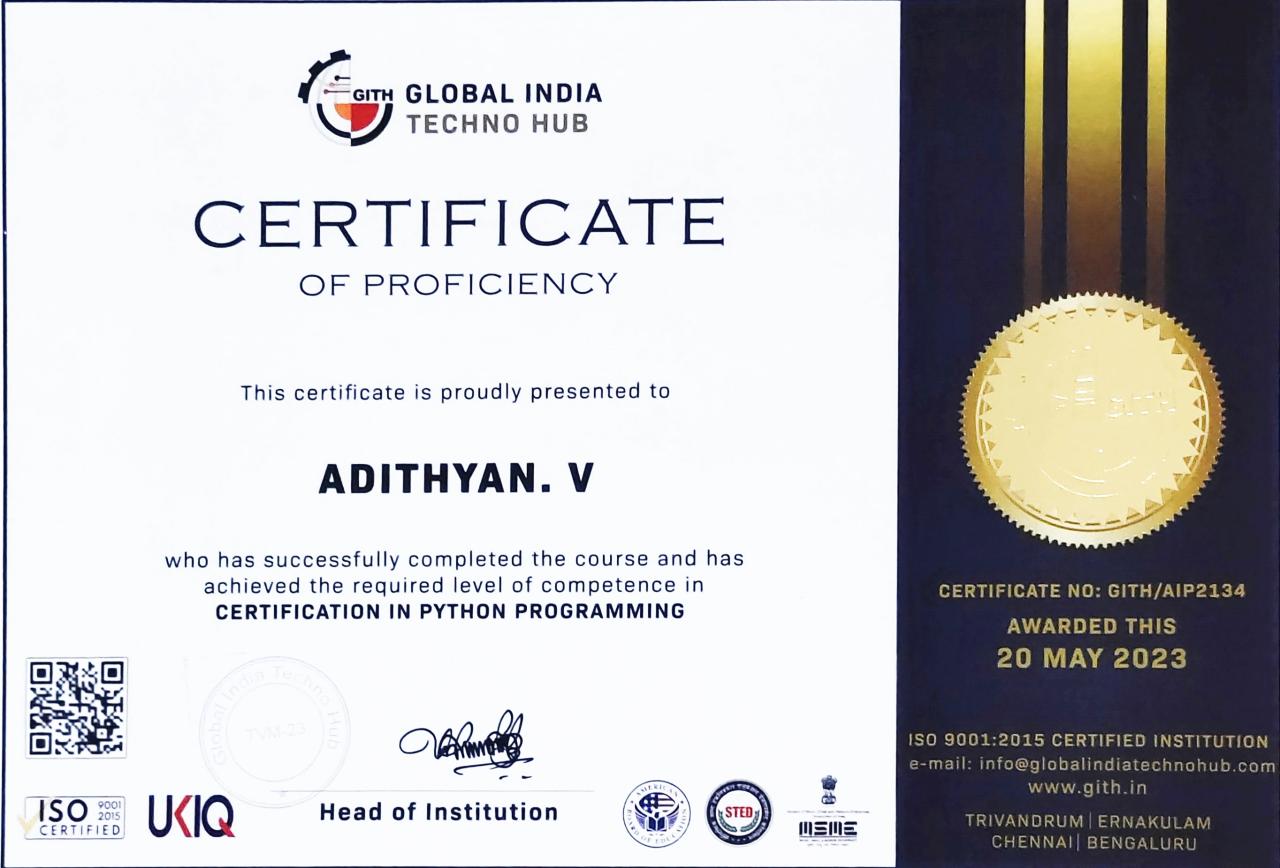
Cyber Security & Cloud Computing
Global India Techno Hub
Bachelor of Computer Applications
Indira Gandhi College of Arts & Science
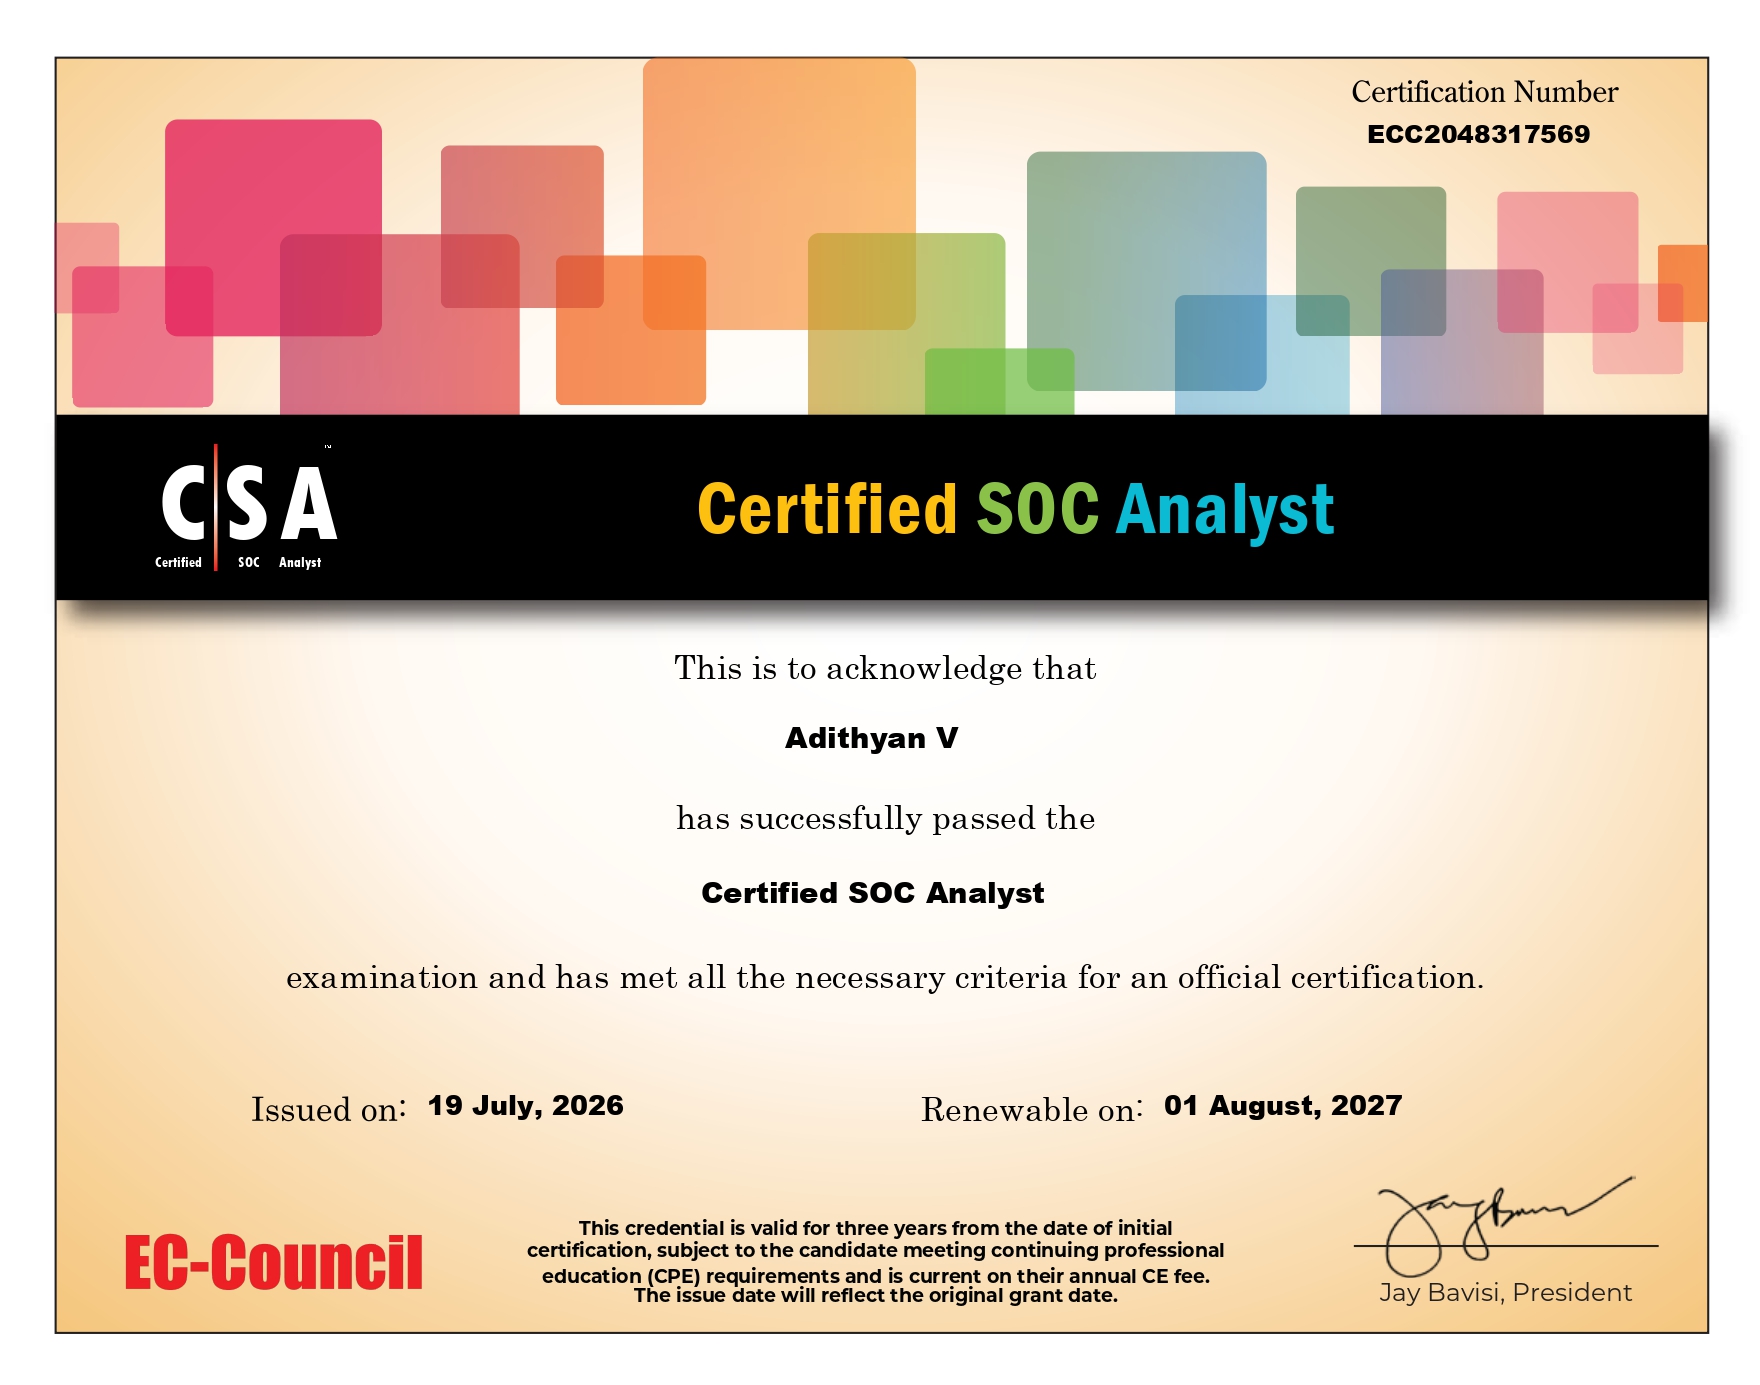
Certifications
Verified credentials and global industry accreditations
Experience
Practical industry engagements and roles
Cyber Security Intern
Future Interns
Completed a 1-month Cyber Security Internship with practical projects covering VAPT, API security validation, and email phishing detection systems.
Cyber Security with AI Intern
NIIT Foundation & Cisco NetAcad
Completed a 1-month Cyber Security Internship with hands-on Cisco enterprise network design, packet routing audits, and earned 3 Cisco certifications.